Seoul National University Hospital has not filed a mandatory cybersecurity disclosure for years, an investigation has found. While tertiary hospitals are generally required to submit such disclosures, the hospital is exempt because it is classified as a public institution.
The concern is that Seoul National University Hospital has a track record of serious data breaches — most notably a North Korean cyberattack that exposed the personal information of some 830,000 patients and staff. As cyberattacks on domestic medical institutions surge, critics say the hospital's approach to information security has been dangerously complacent.
Seoul National University Hospital is the only one among the so-called Big 5 hospitals to have gone without filing a cybersecurity disclosure from 2022 through this year.
By contrast, Severance Hospital, Seoul St. Mary's Hospital, Asan Medical Center and Samsung Medical Center have each filed annual cybersecurity disclosures since 2022, reporting figures such as the number of dedicated information security staff and the level of investment in that area.
The cybersecurity disclosure system was introduced to protect users' right to information and encourage companies to invest in data protection. Tertiary hospitals are included as mandatory filers given the sensitive medical data they handle.
Seoul National University Hospital has been able to sidestep the requirement because it is classified as a "miscellaneous public institution." Public institutions, small and medium-sized enterprises, financial companies and some electronic financial businesses are all exempt from the mandatory disclosure regime. The hospital falls under the Act on the Management of Public Institutions, which grants it that classification and the accompanying exemption.
The problem is that personal data leaks at Seoul National University Hospital have occurred with troubling regularity. In 2021, a North Korean hacking group breached the hospital's systems and stole the personal information of approximately 830,000 people, including patients and current and former employees.
Regarding the incident, police said the North Korean hacking group had planted malicious software in a vulnerable web bulletin board on the hospital's network to extract the data. Investigators also said the IP addresses traced to the attack matched those used in previous North Korean hacking cases.
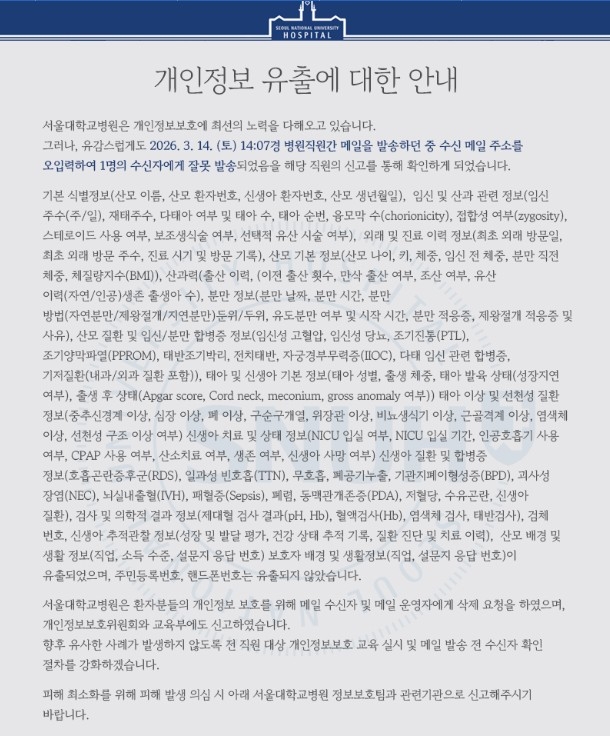
In March this year, a staff error led to another leak, exposing sensitive medical records alongside personal details such as the names, dates of birth and gestational ages of expectant mothers.
Notably, other hospitals not subject to the mandatory disclosure requirement — including Bundang Seoul National University Hospital and other national university hospitals — voluntarily file cybersecurity disclosures, citing their responsibility as handlers of sensitive medical data.
Seoul National University Hospital has maintained that it discloses relevant information through Alio, the government's public institution information portal. But medical sector observers say that given the hospital's history of data breaches, the approach falls short. The hospital said it "discloses relevant information through Alio" but added that it plans "to begin filing a separate cybersecurity disclosure starting next year."
A medical industry official said the hospital "is exempt from the mandatory cybersecurity disclosure requirement due to its designation as a miscellaneous public institution," adding that "given the hospital's standing in the country, its history of being hacked by North Korea and its record of personal data leaks caused by staff errors, it should be taking a more proactive approach to cybersecurity disclosure."
Meanwhile, cyber threats targeting medical institutions — including ransomware attacks — are on the rise. According to data published this year by the Korea Social Security Information Service, the number of cyberattack incidents at domestic medical institutions nearly quadrupled, rising from 18 cases in 2020 to 71 in 2024.
Cumulative losses to medical institutions from such incidents are projected to reach 1.53 trillion won ($1.11 billion) over the next five years.
ko@heraldcorp.com