FSC faces National Assembly audit Thursday — 5 days after breaches
Shinhan: 25,000 records; Kookmin: 119; Hana: 89; Woori, NH NongHyup also hit
PPP vows to grill regulators on oversight failures; calls to summon bank CEOs revive
A string of cyberattacks on major South Korean banks has thrust financial-sector security and regulatory oversight to the center of an upcoming parliamentary audit, with the National Assembly's Political Affairs Committee set to question the Financial Services Commission on Thursday.
The attacks struck Shinhan Bank, KB Kookmin Bank and Hana Bank in quick succession in the days leading up to the audit, raising alarm that the incidents represent a coordinated, sector-wide threat rather than isolated security failures. The People Power Party said it would use the hearing to scrutinize both the FSC's pre-incident supervision and its response after the breaches came to light.
According to financial industry sources, confirmed data leaks have occurred at Shinhan Bank, KB Kookmin Bank, Hana Bank and BNK Busan Bank. Shinhan Bank saw the personal and loan-related information of about 25,000 customers exposed, while KB Kookmin Bank lost data on 119 customers and Hana Bank on 89. At BNK Busan Bank, personal information belonging to 11 outsourced development staff was compromised. Woori Bank and NH NongHyup Bank were also targeted but have not confirmed any customer data leaks so far.
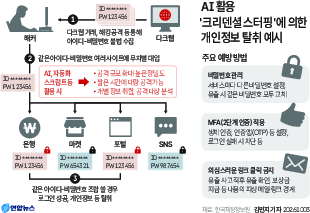
The attackers focused on externally accessible inquiry services and internal employee support systems. Shinhan Bank's loan-agent inquiry service, KB Kookmin Bank's mobile employee support system and Hana Bank's sales support system were each targeted. Industry officials are watching whether AI agents were used to automatically scan for exposed systems and vulnerabilities, though the Financial Supervisory Service is still investigating the extent to which AI was actually employed in each incident.
Financial authorities moved quickly once the scale of the attacks became clear. The FSC convened an emergency response meeting on Friday, bringing together the Financial Supervisory Service, the Korea Financial Security Institute and representatives from major banks and card companies, and ordered a comprehensive review of all externally accessible IT systems. Authorities said they would verify the scope of external exposure, authentication frameworks and whether authentication steps were bypassed during personal data queries, and would share information on attack-linked IP addresses and intrusion attempts across financial institutions.
In political circles, the fact that a full-scale review was launched only after the breaches occurred is expected to become a flashpoint at the audit. Park Sung-hoon, chief spokesperson of the People Power Party, said in a statement Saturday that "bank security is the last line of defense for the financial system that protects the assets and credit of the public," adding that the incidents should be seen as "a warning signal to the defense network of South Korea's financial security, going beyond a simple personal data leak."
The PPP said it would press regulators at the audit on whether their routine supervisory mechanisms had functioned properly. Because multiple banks' externally exposed systems were attacked around the same time, lawmakers are expected to question not only individual banks' security failures but also whether the FSC and the Financial Supervisory Service had identified or flagged the relevant risks in advance.
The question of whether bank CEOs should be called to testify is also resurfacing. Most major commercial bank chiefs were not included in the committee's initial witness list, but Rep. Park Sang-hyeok and others have raised the need to summon the heads of the five largest banks. With the hacking incidents emerging as a major issue just before the audit, whether additional witnesses will be added has become a focus of political attention.
Police have launched a preliminary investigation into the data breaches at Shinhan Bank, KB Kookmin Bank, Hana Bank and BNK Busan Bank. The audit is now expected to examine not only individual banks' security vulnerabilities but also whether the financial supervisory framework is adequately equipped to handle new forms of AI-assisted attacks, and how quickly the affected institutions identified and reported the incidents.
hong@heraldcorp.com