KB, Shinhan, Hana, Woori, NH NongHyup Financial reviewed
'Financial security must be proven through investment and results'
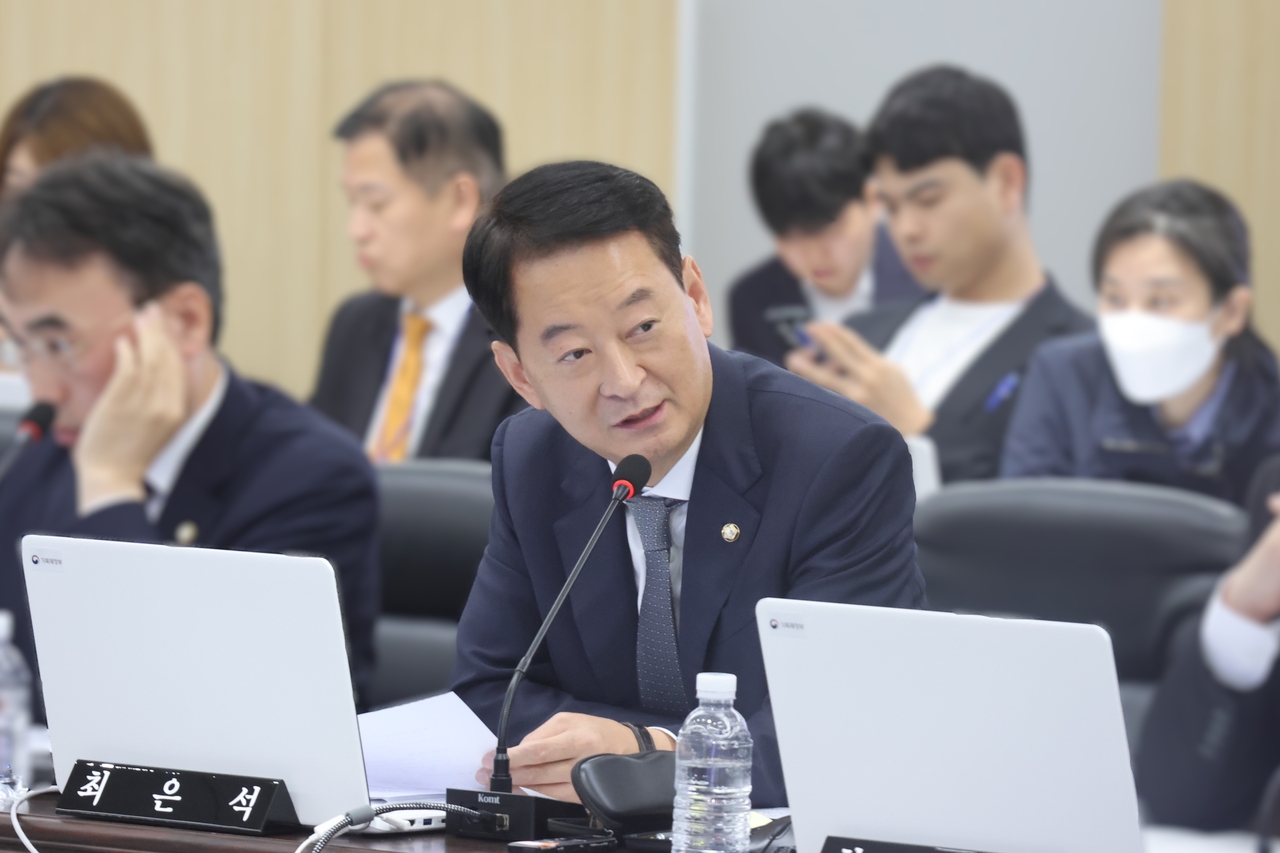
People Power Party lawmaker Choi Eun-seok has reviewed the cybersecurity frameworks of South Korea's five largest financial holding companies amid a string of hacking and information security incidents in the financial sector. He examined not only how security budgets are allocated but also how they are actually spent, how specialist personnel are deployed and how incident prevention systems are structured, and called on the groups to strengthen their information security capabilities.
Choi, a member of the National Assembly's Political Affairs Committee, said Monday he had recently met with the chief information security officers of KB, Shinhan, Hana, Woori and NH NongHyup Financial to review the state of information security across the financial sector.
The review was arranged to assess whether security investment, staffing and incident response systems at the holding-company level are adequate to handle real-world risks, at a time when financial firms are accelerating their digital transformation and cyber threats are growing more sophisticated.
Choi examined not only the scale of information security budgets but also spending rates, investment priorities and progress on upgrading outdated security systems and addressing vulnerabilities. The underlying message was that the effectiveness of security investment should be measured not by budget size but by how much actual security risk has been reduced.
He also reviewed how financial security specialists are recruited and deployed — looking at the size of dedicated security teams at each firm, how responsibilities are divided and what training programs exist to build expertise — and urged the companies to continuously strengthen the professionalism and on-the-ground response capabilities of their security organizations.
Information security governance between holding companies and their subsidiaries was also a key area of review. Choi examined incident reporting and response procedures and whether recurrence-prevention measures are being followed, and said integrated risk management at the financial group level — rather than reliance on individual subsidiaries — is necessary.
Because banks, card companies, brokerages, insurance firms and other subsidiaries under each financial holding company share digital infrastructure and business systems, he said the groups must prepare for the possibility that a security vulnerability at one subsidiary could cascade into a risk for the entire group.
He also stressed the need to strengthen preventive systems rather than focus on damage control after an incident occurs, saying that regular security vulnerability assessments, simulation drills and employee information security education must go beyond formality and translate into swift responses when actual breaches occur.
"Information security at financial firms is not a cost item managed by the IT department — it is a core management challenge that protects customers' assets, their personal information, and ultimately the financial firm's own credibility," Choi said. "Every time a financial incident occurs, firms promise to expand security investment and put recurrence-prevention measures in place. What matters is whether those promises actually lead to real budget execution, expanded staffing and improved security on the ground."
He added that a financial firm's security level cannot be judged solely by the absence of incidents. "What matters is how thoroughly you prepared in normal times to prevent incidents, and how quickly you can respond when a threat materializes," he said. "The five major financial holding companies must take a leading role in raising the standard of information security across the financial sector."
"A financial firm that cannot protect its customers' money and information cannot earn trust no matter how strong its earnings are," Choi said. "Financial security is not an optional investment — it is a matter of survival that determines whether a financial firm can continue to exist. Holding company chairmen and executives must take personal responsibility and actively push forward on real budget execution, expanding specialist staffing, and field-centered education and training."
mp1256@heraldcorp.com