FSS, Korea Financial Security Institute run program once a year; KISA evaluates quarterly
Reward pool roughly one-sixth of KISA's
FSS expands bug bounty targets from 34 to 70 firms this year
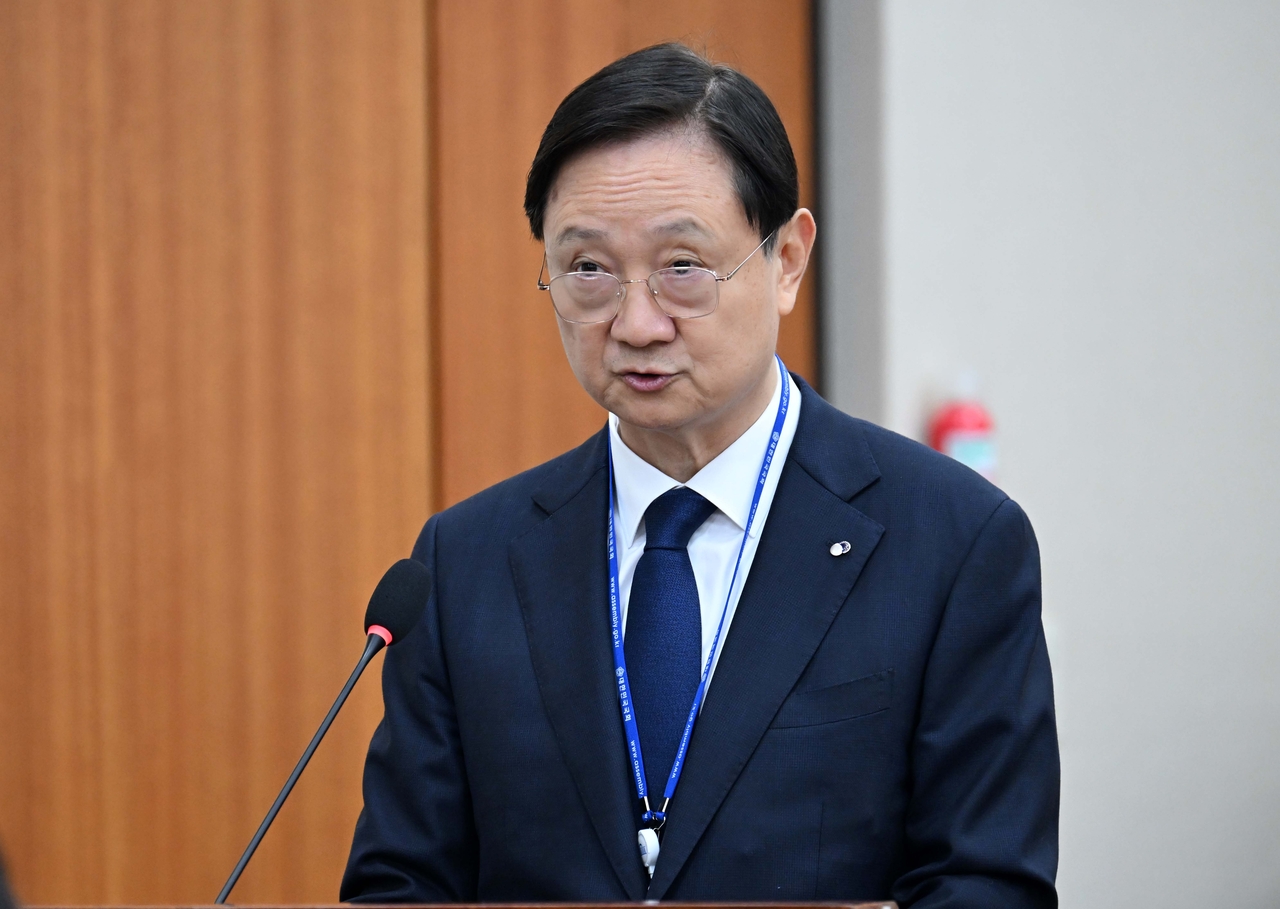
Financial Supervisory Service Director General Lee Chan-jin said Monday he would expand the financial sector's bug bounty program — which proactively identifies security vulnerabilities — to at least the level of the Korea Internet & Security Agency.
Lee made the pledge at a National Assembly audit by the Political Affairs Committee on Monday, after Democratic Party of Korea lawmaker Han Min-su pointed out that the FSS and the Korea Financial Security Institute had underperformed KISA in running their bug bounty programs. "We will raise the standard to match KISA's — and aim to go beyond it," Lee said.
Under a bug bounty program, external security experts report vulnerabilities they find in financial institutions' systems, which are then verified and rewarded with prize money.
According to Han, KISA has operated a bug bounty program since 2012, conducting quarterly evaluations every March, June, September and December. Comparative data showed the agency received 1,786 reports, recognized 670 vulnerabilities and paid out a total of 276.69 million won ($206,000) in rewards.
By contrast, the joint FSS–Korea Financial Security Institute bug bounty program runs only once a year. It received 249 reports, recognized 164 vulnerabilities and paid out around 44.2 million won in rewards — roughly one-sixth of KISA's payout.
The FSS this year expanded the number of financial firms covered by the bug bounty program from 34 to 70, adding virtual asset service providers and general insurance agencies to the list for the first time. The number of firms subject to blind penetration testing was also doubled from 20 to 40, and red-teaming exercises — designed to check for information leaks and abnormal responses that can arise from generative AI services — were added to the training scope.
Following a series of cybersecurity breaches in the financial sector in recent months, the FSS plans to continue expanding the scope of hands-on security drills, including bug bounty programs and penetration testing.
rim@heraldcorp.com