Data breach detected in internal work systems
No personal or credit information of general customers exposed
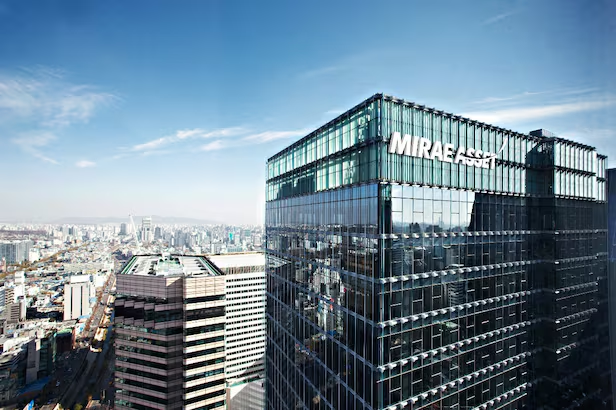
Mirae Asset Global Investments said Wednesday that data had been leaked from some of its internal work systems through unauthorized external access, but that no personal or credit information belonging to general customers was compromised.
The company said it recently detected signs of abnormal access via external internet protocol (IP) addresses in some of its web systems. Unauthorized parties viewed data without legitimate access credentials, though no malware infection or service disruption occurred.
"Based on what has been confirmed so far, the scope of the leak is limited to information used in certain internal work systems," the company said. "Unique identification details — including resident registration numbers, passport numbers, driver's license numbers and alien registration numbers — as well as sensitive information and personal credit information were not leaked."
The company said the affected systems are not services operated for individual customers, meaning general investors' information was not among the data exposed. No financial damage was incurred, and there is no evidence of direct intrusion into servers or databases. The company's website and other key systems and services are operating normally.
The company blocked the relevant access routes, activated an emergency response protocol and filed an incident report with the Financial Services Commission and the Financial Supervisory Service. It is currently conducting a detailed investigation into the cause and scope of the breach with the help of an external cybersecurity firm.
"There was a data leak caused by abnormal access from an external IP address in some of our systems, and we have blocked the access route and are conducting an analysis," a Mirae Asset Global Investments official said. "We completed security measures addressing the vulnerability immediately upon detecting the incident, and we plan to work closely with an external cybersecurity firm to thoroughly analyze the cause and take all necessary steps to prevent a recurrence."
A string of hacking and data breach incidents that began in the banking sector has been spreading to the financial investment industry. Daishin Securities said Wednesday morning in a press release that the personal and credit information of 38,490 customers had been leaked.
Virtual asset exchange Bithumb also said it became aware Tuesday that personal information had been leaked through unauthorized external access to its internal mobile groupware system. The company is currently analyzing the exact scope of the breach, including the possibility that member information was affected.
Financial Supervisory Service Governor Lee Chan-jin said at the opening of a regular meeting with the board chairs of eight banking holding companies Wednesday morning that he understood "a widespread hacking incident occurred at major financial investment firms on Tuesday," and urged the financial sector to strengthen IT security.
moon@heraldcorp.com