Breach affects former Interpark Tour customers
Nine data fields exposed, including names and stay dates
Security gap found in major domestic travel platform
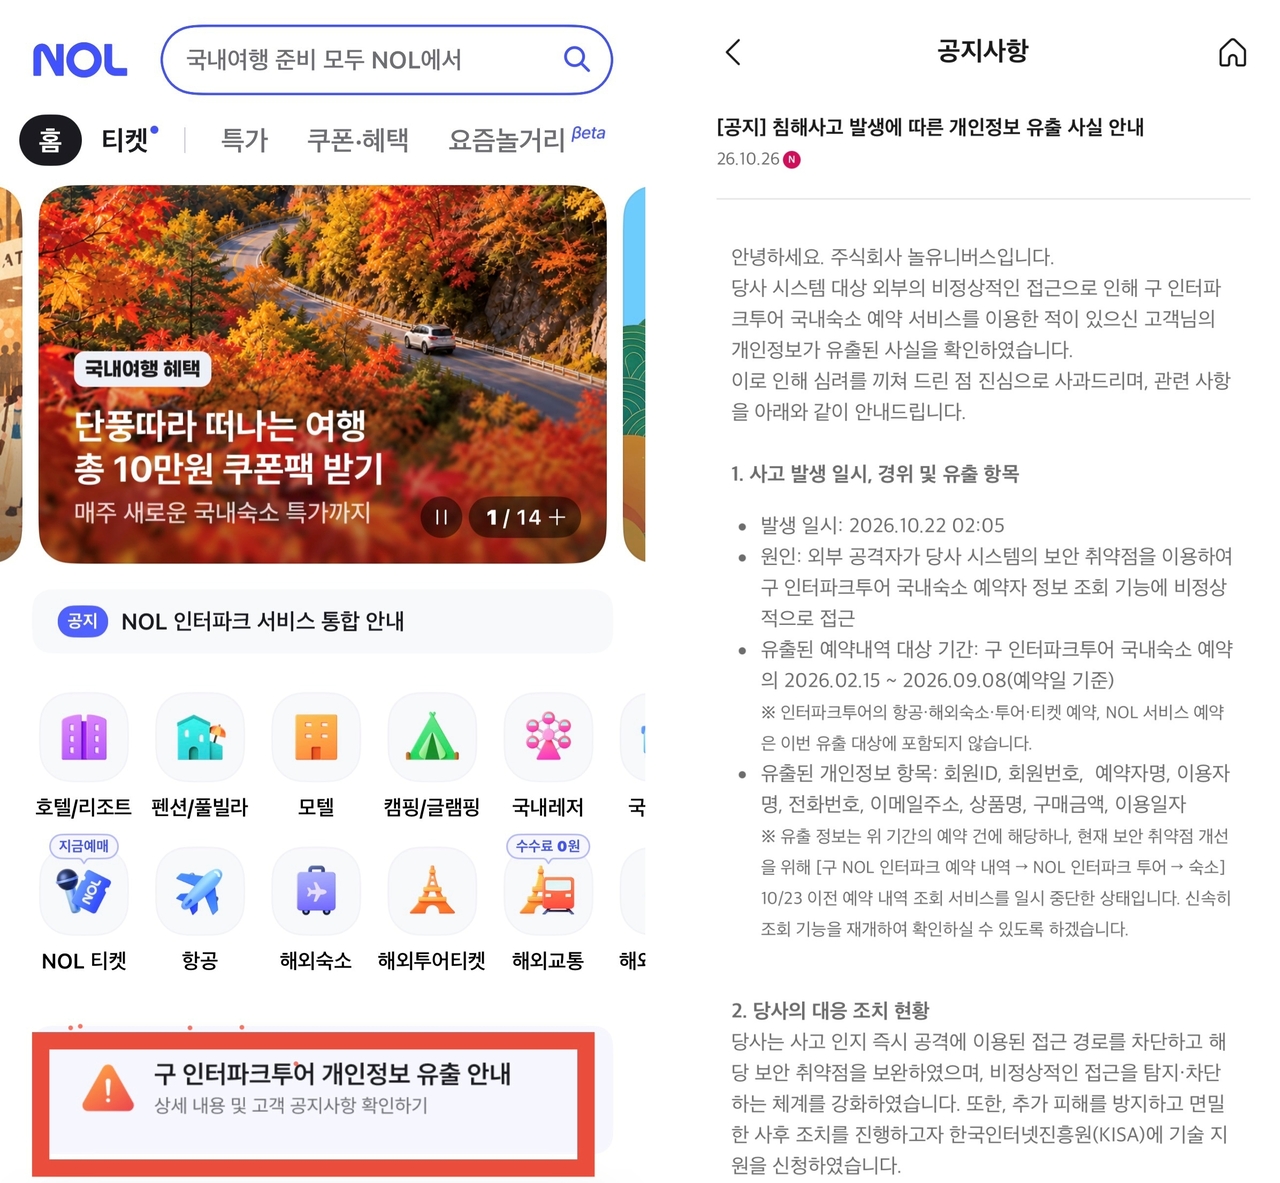
Personal information of customers who made domestic accommodation reservations through the former Interpark Tour platform, now operated by Nol Universe, was leaked over a roughly seven-month period, the company confirmed. The exposed data included bookers' names and contact details, as well as the names of products reserved, purchase amounts and check-in dates.
According to a notice titled "Notification of personal information leak following a security breach" posted Monday on Nol Universe's official website, the incident occurred at 2:05 a.m. Thursday at the former Interpark Tour service.
The company said an outside attacker exploited a security vulnerability in its systems to gain unauthorized access to a function that allows users to look up domestic accommodation reservation details on the former Interpark Tour platform.
The breach covers domestic accommodation bookings made between Feb. 15 and Sept. 8 this year. However, reservations for flights, overseas accommodations, tours and tickets through Interpark Tour, as well as bookings made through the Nol service, were not affected.
Nine categories of data were exposed: member ID, member number, booker name, guest name, phone number, email address, product name, purchase amount and check-in date. The company did not disclose the number of affected customers or the total number of reservations involved.
Nol Universe has temporarily suspended the reservation history lookup service for bookings made before Thursday under the accommodation menu in the "former Nol Interpark booking history" section while it works to address the security vulnerability.
"Upon becoming aware of the incident, we immediately blocked the access route used in the attack, patched the vulnerability, strengthened our anomalous-access detection system and applied to the Korea Internet & Security Agency for technical support to prevent further damage," the company said in the notice. It also informed affected users that they may seek civil damages or statutory compensation under the Personal Information Protection Act, and that they can pursue remedies through the Personal Information Dispute Mediation Committee or the Personal Information Infringement Report Center.
Just days before this large-scale breach, Nol Universe had disclosed a separate attack on Tuesday that exposed the personal information of two users, some employees and associates at partner companies. The data leaked in that incident included names, phone numbers, corporate email addresses and employee identification numbers.
In Monday's notice, Nol Universe said it would "continuously strengthen its security systems" and apologized, saying it was "sincerely sorry again for the concern this incident has caused."
terry@heraldcorp.com