Companies using ERP software Smart A 10 face potential data exposure
Breach could ripple to clients of Douzone Bizon's own customers
Douzone Bizon says it followed legal procedures in notifying authorities
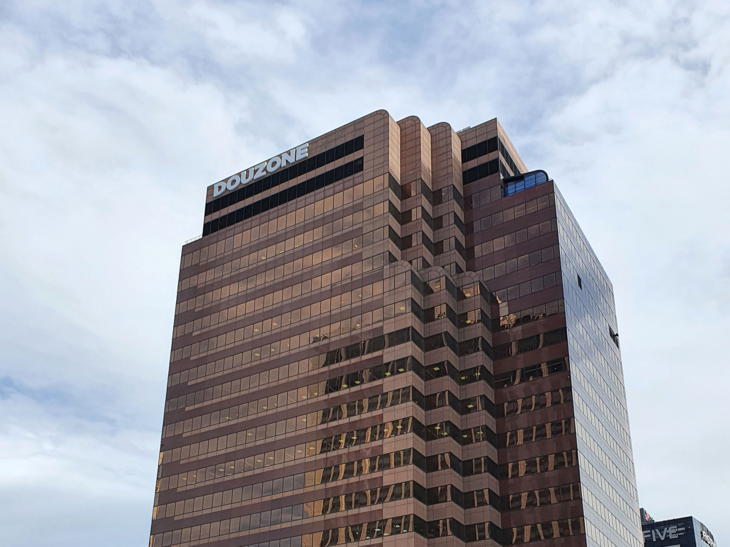
Concerns are mounting that up to 110,000 corporate customers of Douzone Bizon, a provider of enterprise software services, could be caught in the fallout from a cyberattack on the company, with personal data potentially exposed.
More than 110,000 companies use Smart A 10, the enterprise resource planning system Douzone Bizon operates. The company has acknowledged that some personal information managed through Smart A 10 may have been leaked.
According to industry sources Monday, Douzone Bizon issued a "notice of possible personal data breach and security incident" on Oct. 18, disclosing that attackers had gained unauthorized access to internal systems through its development server and that records of data queries had been detected. The company said the personal data potentially exposed included names, resident registration numbers (with the last six digits encrypted), bank account numbers (encrypted), addresses, mobile phone numbers and email addresses held by some Smart A 10 users.
As a result, up to 110,000 companies using Smart A 10 are expected to be affected by the breach. The scale of the leak remains unclear, as Douzone Bizon itself said it has so far been "unable to identify specific customers or data subjects whose information may have been leaked."
According to Douzone Bizon, Smart A 10 is used by more than 90 percent of small and medium-sized enterprises and tax accounting firms in South Korea, and is an ERP system optimized for corporate accounting.
Douzone Bizon has said that "more than 110,000 companies use Douzone Smart A 10" and that it "can be applied to all companies in South Korea with its standardized functions and processes." That reach means the breach could extend beyond Douzone Bizon's direct customers to the clients of those customers as well.
That breadth is also seen as the reason the Ministry of Science and ICT classified the Douzone Bizon hack as a "serious incident."
The ministry said in an unscheduled press release Sunday that it had convened an emergency meeting of its cybersecurity incident review committee under the Act on Promotion of Information and Communications Network Utilization and Information Protection, and that the panel had concluded the breach constituted a serious incident requiring the formation of a joint public-private investigation team.
Douzone Bizon's decision to post a notice on its website rather than directly inform affected individuals also draws fire.
The Personal Information Protection Act requires companies, upon learning of a possible data breach, to notify all affected individuals of information needed to minimize harm, taking into account the type of personal data involved, the impact on data subjects and the degree of risk.
The intent of the provision is to alert those affected as early as possible so that damage can be kept to a minimum.
On the question of notifying customers, Douzone Bizon said: "Immediately after signs of an anomaly were detected in our systems, we conducted a swift internal investigation and, in accordance with legally prescribed procedures, filed reports with the Korea Internet & Security Agency and the Personal Information Protection Commission, and posted a notice on our website."
ko@heraldcorp.com