Overhaul enforces full access verification and least-privilege rules
App signing keys and DRM keys replaced to strengthen data protection
AI-based threat detection technology to expand real-time response
Tving has rebuilt its security framework around a zero-trust model, tightening its breach-response systems under a policy of verifying all access requests and accelerating the adoption of next-generation AI-based security technology.
The streaming service said Wednesday it had established a zero-trust security framework that treats no access as inherently trustworthy, continuously verifying users, devices and permissions.
Tving designated four core principles for the framework: strict access verification, least privilege, assumed breach and continuous validation. The company plans to apply these principles across its service and cloud environments.
To enforce strict access verification, Tving applied authentication token checks across all app and web channels and introduced mandatory updates for older app versions. It is also reviewing the adoption of technology to detect and block tampered apps.
Under the least-privilege principle, the company broke down system access rights by job function and put in place systematic controls over the scope and validity period of each permission.
Tving is also reviewing its incident-response procedures by scenario under an assumed-breach approach. For continuous validation, it set up a system to detect anomalous activity in its cloud environment in real time and receive alerts on abnormal access attempts.
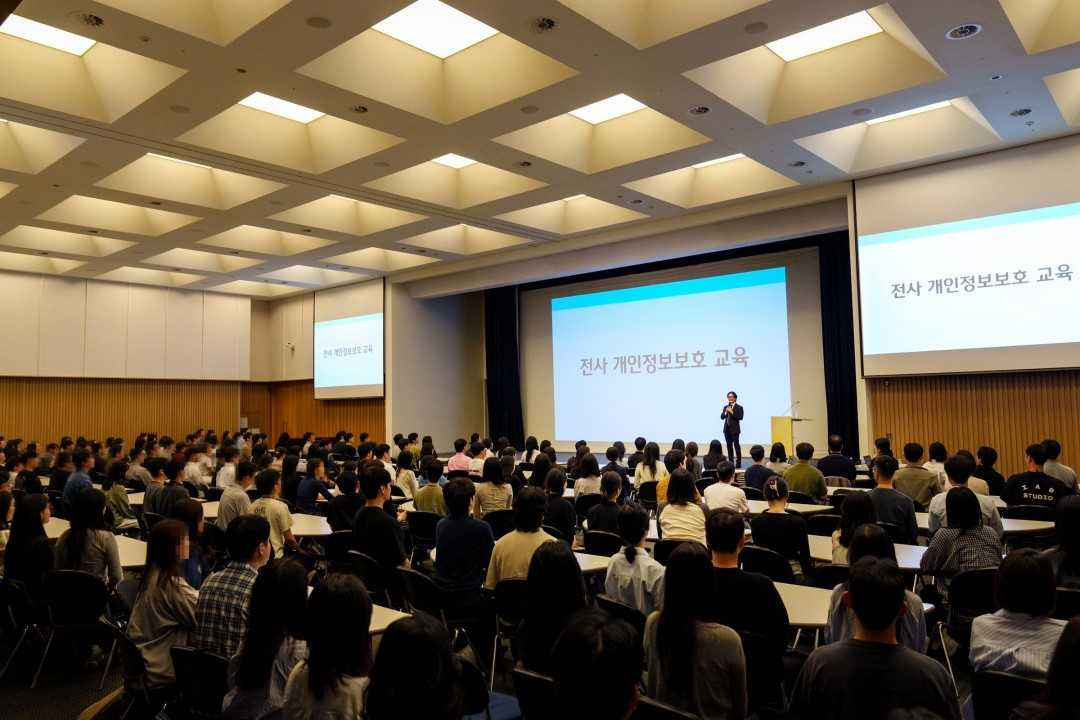
Tving plans to pursue follow-up measures to further strengthen its zero-trust framework. These include evaluating credential management tools and solutions for source code analysis and vulnerability management, expanding the scope of penetration testing and vulnerability assessments to cover cloud accounts and access privileges, upgrading scenario-based incident-response procedures, and reviewing the introduction of a bug bounty program.
The company also plans to build out a next-generation security governance framework, reinforcing its integrated cloud security inspection system and deploying AI-based threat detection and blocking technology.
Tving has also overhauled key security areas. It migrated secrets embedded in code to a dedicated management system and established automated blocking and anomalous-access detection at the source code storage stage. Next-generation endpoint detection and response (EDR) solutions have been deployed across all employee devices.
The company said it has also raised the level of customer data protection. It replaced app signing keys and digital rights management (DRM) keys across the board, upgraded its login and session verification architecture, and is transitioning to a bcrypt-based password storage algorithm.
"We are continuously reviewing our security framework with customer data protection as our top priority, and we are strengthening our overall security posture," a Tving official said. "We will continue to upgrade our access and privilege management and incident-response systems based on zero-trust principles, and sustain investment in next-generation security technology."
chami@heraldcorp.com