Hacking incidents spread from banks and savings banks to online lending platforms
Korea Fintech Industry Association shares attack case studies
Industry calls for government vouchers to cover ISMS-P certification costs
Network separation rules restrict smaller firms from AI-based defenses
A wave of cyberattacks targeting South Korea's financial sector has pushed fintech companies to tighten their defenses, even as legislation meant to strengthen information security obligations has stalled in the National Assembly for more than 10 months. Small and midsize fintech firms are calling on the government to subsidize security investment costs and ease regulations that restrict the use of AI-based security tools.
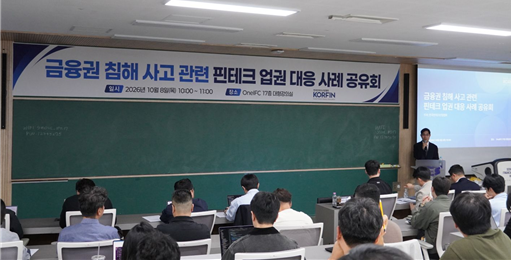
The Korea Fintech Industry Association held a case-sharing session Thursday at One IFC in Yeouido, Seoul, bringing together security and IT officials from electronic financial service providers and association member companies.
Participants reviewed the key contents of an IT security checklist that the Financial Services Commission had asked the fintech industry to use for self-assessments, and discussed the need to strengthen security checks across the sector.
The session also covered concrete breach-prevention measures drawn from real-world cases of both successful and failed hacking attempts against electronic financial service providers. Measures discussed included requiring additional authentication for system access through external channels such as merchant networks, blocking attacker IP addresses, reviewing past access logs, checking for vulnerabilities in externally exposed systems, and monitoring for abnormal access.
"The security incidents occurring in the financial sector recently are not a problem confined to any one company or segment — they are directly tied to the trustworthiness of financial services as a whole," Korea Fintech Industry Association Chairman Kim Jong-hyun said. "It is important not just to respond after an incident occurs, but to build a system that identifies risk factors in advance and responds proactively."
Calls grow for Electronic Financial Transactions Act revision, but certification costs weigh on smaller firms
Despite mounting pressure to strengthen financial sector security, the legislative push to back it up has lost momentum. An amendment to the Electronic Financial Transactions Act, introduced by Democratic Party of Korea lawmaker Yoo Dong-su on Nov. 28 last year, was referred to the National Assembly's Political Affairs Committee in March but has remained at the subcommittee review stage ever since.
The bill would designate a financial company's CEO as the ultimate person responsible for ensuring the safety of electronic financial transactions and would expand the authority of chief information security officers. It also seeks to introduce a disclosure regime requiring financial companies to make public their information security investment and management practices.
The bill would also allow regulators to impose fines of up to 3 percent of total revenue when transaction or personal credit data is leaked in a breach, and to levy a compulsory compliance fee of up to 50 million won ($37,300) on companies that fail to carry out remediation or corrective orders following vulnerability assessments.
Still, voices within the fintech industry say smaller operators need targeted support to manage the financial burden. "It is true that small and midsize fintech companies can feel the strain," an industry official said. "Since obtaining ISMS-P certification also comes with costs, it would be helpful if the government first put in place a support mechanism — such as providing vouchers."
Network separation rules eased, but smaller fintech firms still face high barriers
There are also calls to reform regulations that hamper AI-based defenses against increasingly sophisticated cyberattacks. Using external AI services to rapidly identify security vulnerabilities could be blocked by network separation rules, which require financial companies to keep their internal networks isolated from the public internet.
The FSC last month expanded the pool of companies eligible to apply for an exemption from network separation rules for AI security testing, raising the number from 49 to 75. However, it postponed the selection of second-round participants — originally scheduled for Wednesday — to allow time to respond to the recent financial sector hacking incidents and conduct additional security reviews.
Electronic financial service providers must meet certain conditions to qualify, including having annual electronic financial transaction volumes of at least 2 trillion won and deriving more than 10 percent of total revenue from related activities, leaving smaller operators effectively shut out.
"When attacks are powered by AI, it is difficult for humans to respond to each one manually, so defenders must also be able to use AI," an industry official said. "There is a need to review support measures — including easing network separation rules and building shared network infrastructure — so that smaller firms can also access the relevant technology."
snsd@heraldcorp.com
won@heraldcorp.com