FSC holds industry-wide forum ahead of security overhaul
Employee data, customer names, account numbers among leaked information
No confirmed direct financial losses to individual users yet
Lee Eok-won warns of accountability for lax or perfunctory responses
Forty cybersecurity breaches at 37 financial firms were reported in the roughly one month since late September, leaking more than 473,000 records, authorities said Thursday. About 1 billion won ($746,000) in funds managed by some electronic financial service providers, virtual asset businesses and online investment-linked finance companies — known as P2P lenders — was stolen outright. No account passwords or other information likely to enable fraudulent transactions has been confirmed as leaked, and no individual users have yet suffered direct financial losses.
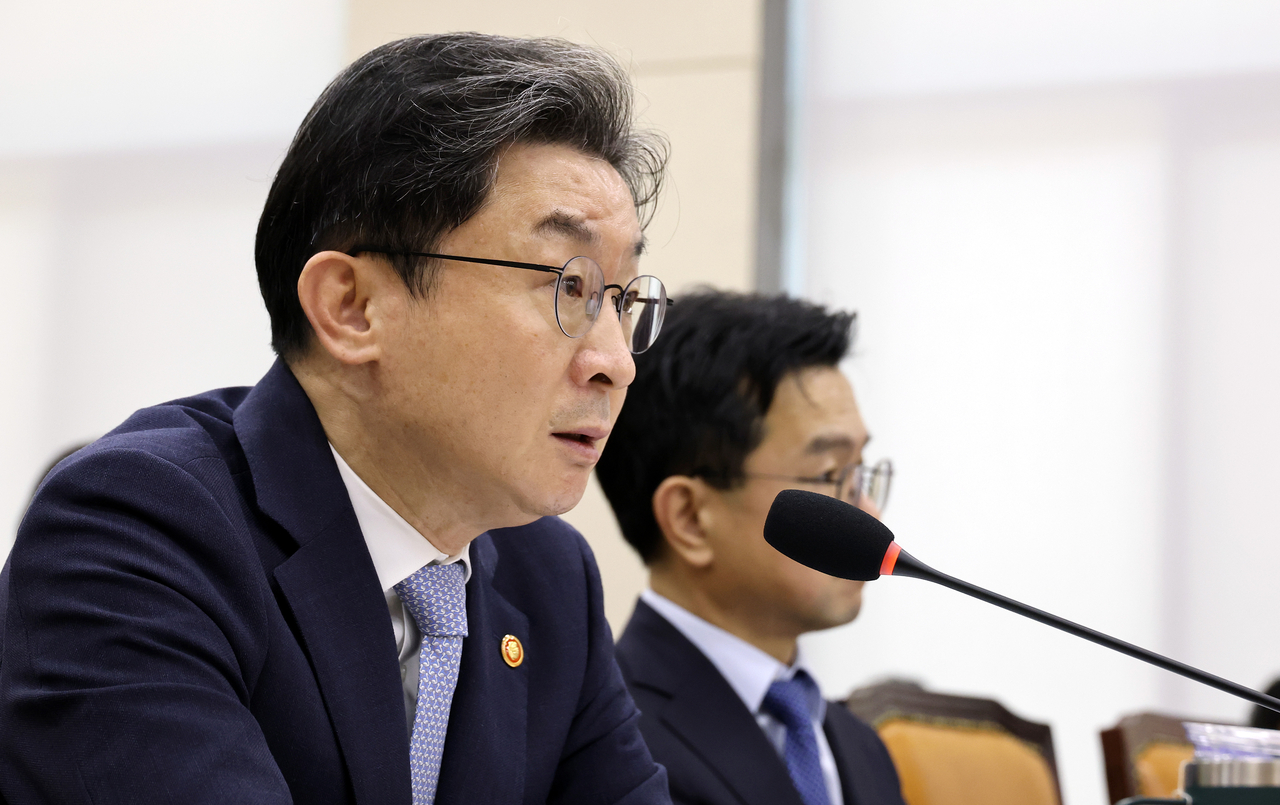
The Financial Services Commission convened an industry-wide forum Thursday, chaired by FSC Chairman Lee Eok-won and attended by officials from the Financial Supervisory Service and the Korea Financial Security Institute as well as heads of financial industry associations, to review the recent wave of breaches and discuss countermeasures.
According to the FSC, a total of 40 incidents were reported across 37 companies between Sept. 30, when breaches first began to be confirmed, and Tuesday. By sector, electronic financial service providers accounted for the most cases at 10 firms, followed by financial investment companies and savings banks at five each. Banks and P2P lenders each had four firms affected, while insurers and virtual asset businesses each had three. Two credit finance companies and one mutual finance institution also reported breaches.
Incidents continued even after a checklist-based security review covering the entire financial sector concluded on Oct. 14. Subsequent breaches were concentrated mainly at small and mid-sized securities firms, insurers, electronic financial service providers, P2P lenders and virtual asset exchanges. The pattern confirmed that the problem extends well beyond traditional financial institutions such as banks, insurers and brokerages to encompass in effect every segment of the financial industry, including electronic finance, P2P lending and virtual assets.
The total volume of leaked information identified so far stands at approximately 473,000 records. The leaked data includes employee information as well as customer names, resident registration numbers and account numbers collected by financial firms in the course of their operations. Authorities said no cases have yet been confirmed in which information that could directly enable fraudulent transactions — such as account passwords — was among the leaked data.
Cases of actual fund theft have also emerged. About 1 billion won in stolen funds has been reported so far at a number of small virtual asset exchanges, electronic financial service providers and P2P lenders. Most cases involved unauthorized transfers from pooled accounts where companies manage customer funds collectively — including virtual asset hot wallets, consumable reward points and P2P lending deposit accounts. Direct financial losses to individual users have not yet materialized, authorities said.
Financial authorities are on alert for the possibility that leaked personal data could be exploited in secondary crimes such as voice phishing, even where no direct monetary damage has been confirmed. They have instructed financial firms to notify customers of the data leaks and to fully implement consumer protection measures — including compensation — should any harm occur, while also stepping up monitoring for abnormal transactions.
FSC Chairman Lee sharply criticized the financial sector's security response at the forum. "We must take a hard look at whether our financial industry is properly fulfilling this basic duty in light of the recent incidents," Lee said. "Keeping customers' money and information safe is the most fundamental reason financial companies exist — a responsibility that cannot be compromised."
Lee also said management must take direct ownership of security rather than waiting to react after incidents occur. "Security is not a technical matter for a specific department — it is a core management responsibility that CEOs must own directly," Lee said. "Failures in security management can go beyond a simple technical failure and become a failure of management itself."
In response, financial authorities plan to conduct comprehensive inspections of IT assets accessible from outside and internal control systems at approximately 580 entities — including financial firms, electronic financial service providers and virtual asset businesses — by year-end. Separate efforts to overhaul the vulnerability assessment regime and improve network-separation regulations will proceed on a parallel track.
"A financial company that cannot protect its customers' information and assets has already lost its reason to exist," Lee said, calling on CEOs across the financial industry to immediately form company-wide emergency response teams and move to strengthen their security frameworks.
rim@heraldcorp.com