FSI head sorry for breach at FISCON opening
Files from 48 financial firms estimated stolen
'AI attack speed made it hard to stop,' official says
AI reproduced vulnerability in 12 minutes; institutions took 43 days to patch
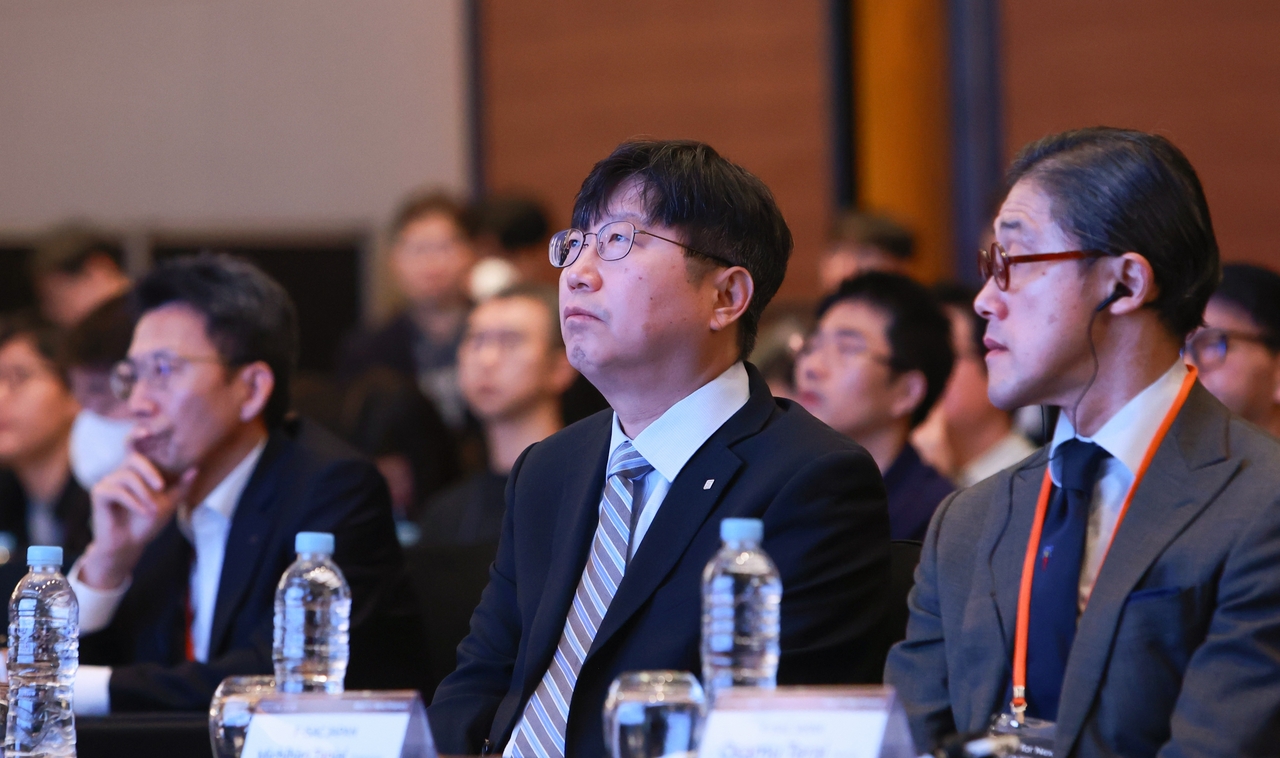
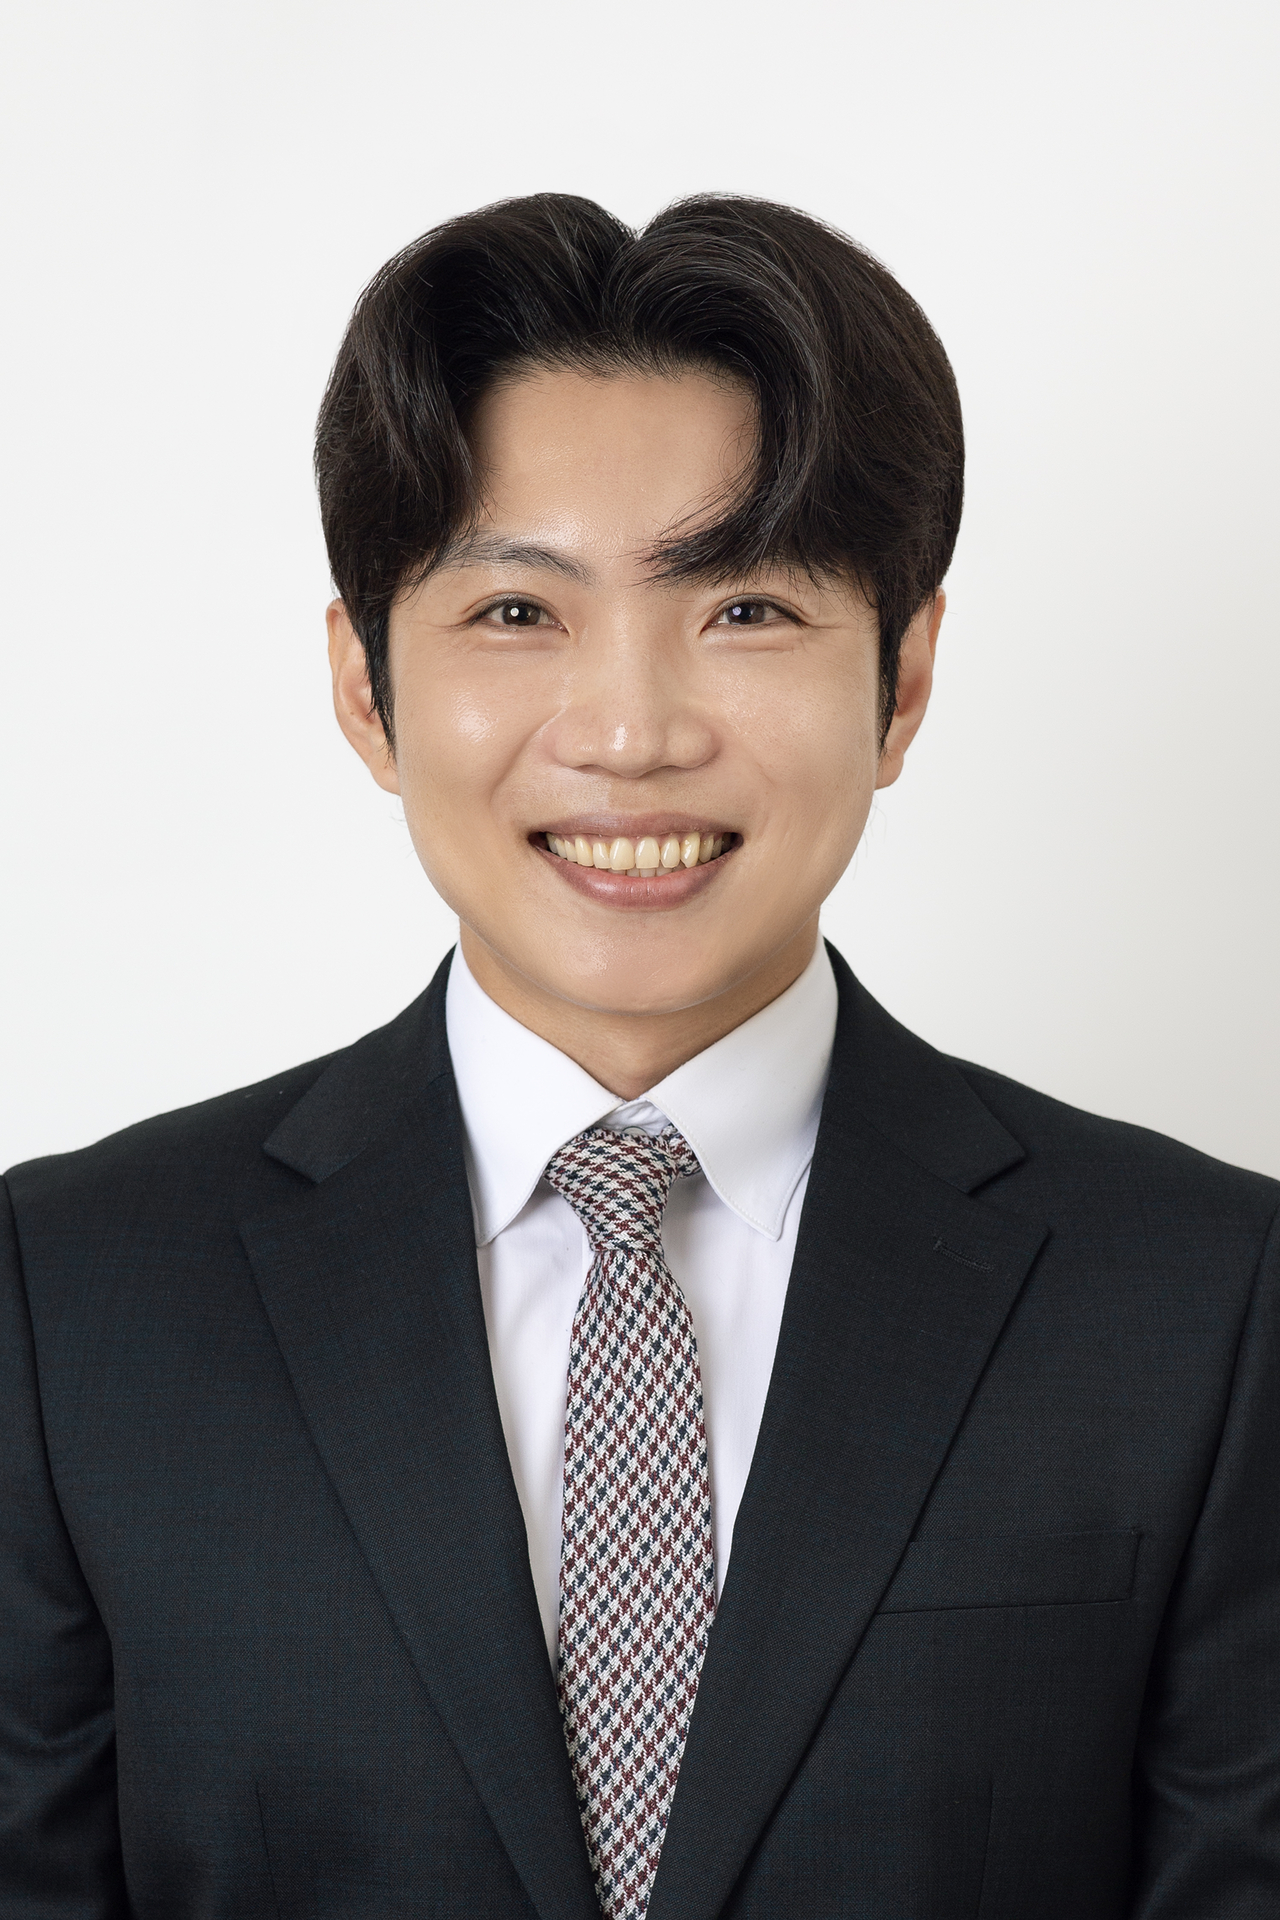
Park Sang-won, president of the Financial Security Institute, publicly apologized Thursday for a hacking incident that compromised the institute's own systems.
Speaking at the opening ceremony of the Financial Information Security Conference (FISCON 2026) at the Conrad Hotel in Yeouido, Yeongdeungpo-gu, Seoul, Park said he was "deeply sorry that this incident occurred despite our obligation, as a specialized financial security agency, to maintain the highest level of security." Park also pledged to determine whether additional data had been leaked, investigate the cause of the breach, conduct a full inspection of all systems and put measures in place to prevent a recurrence.
The Financial Security Institute detected abnormal access Monday on its "continuous information security assessment site," a platform through which financial companies submit evaluation materials, and shut down the service. An estimated 130 or more files belonging to 48 financial firms are believed to have been leaked. Financial regulators are conducting on-site inspections, and police have begun tracing the IP addresses used in the attack.
Officials within the institute acknowledged that the speed of AI-assisted hacking had made the breach difficult to stop. Lee Jin-ho, head of the institute's RED IRIS Team 2, told reporters Thursday that "the speed of AI-driven attacks has increased, and there were aspects of this incident that were simply hard to block."
AI-powered hacking has already become a reality in South Korea's financial sector. Multiple domestic financial firms were targeted by AI-assisted attacks between September and October. Yoo Jae-wook, a senior researcher on the institute's RED IRIS team, said attackers had combined the automated hacking tool ARTEX with several large language models, including DeepSeek, to infiltrate the business systems of financial companies.
Yoo said the nature of AI-assisted attacks had fundamentally changed. "In the past, a person would read code, ask AI when stuck, and then run it manually — but now AI reads the execution results and continues on to the next task on its own," Yoo said. "Even if it fails once, it reads the cause, adjusts the conditions and tries again immediately."
A key strength of ARTEX, officials said, lies in how systematically it manages information gathered during an attack. "There are several reasons ARTEX is effective at finding vulnerabilities, but I believe context management and utilization are central to it," Lee said. The tool links and records web pages, access paths and the results of attack attempts, then draws on that accumulated data in subsequent attacks.
The spread of AI is also widening the speed gap between attackers and defenders. In an external experiment Yoo cited, AI analyzed a publicly released security patch and generated proof-of-concept exploit code in about 12 minutes. By contrast, the median time for organizations to complete vulnerability remediation reached 43 days. "Attack preparation is shrinking to minutes, while protection is still moving on a weekly timescale," Yoo said, calling for layered defense systems that prevent access to critical data even if a single server is breached.
The Financial Security Institute said it has been expanding AI-assisted security assessments. In penetration tests conducted over roughly six weeks from May to July this year across 16 financial firms, AI contributed to identifying 34 of 94 total vulnerabilities found — accounting for 36.2 percent. However, only 34 of the 301 vulnerability candidates flagged by AI — 11.3 percent — passed expert verification. "The high false-positive rate created a significant review burden," Lee said, adding that the AI also showed a tendency to suggest attack paths that could not actually be reproduced.
In response, the institute is improving its proprietary AI inspection technology while developing an integrated framework that connects external penetration testing tools such as ARTEX. The aim is to allow newly emerging tools to be plugged into the existing system without requiring a separate development process each time. The institute is also building a database of vulnerability information accumulated through financial-sector security assessments to improve the diagnostic accuracy of its AI.
"When a high-performing tool emerges externally, a gap opens up while we develop our own technology," Lee said. "We need to strengthen our capabilities so we can find vulnerabilities before the attackers do."
snsd@heraldcorp.com