Security budgets rise amid sector headwinds, yet breaches keep coming
Saemaul Geumgo Central sets aside 16.8 billion won; KDB Capital allocates 6.9 billion won
Savings banks average 6 dedicated security staff, versus 92 at major commercial banks
Attacks mimicking normal user behavior increasingly evade detection
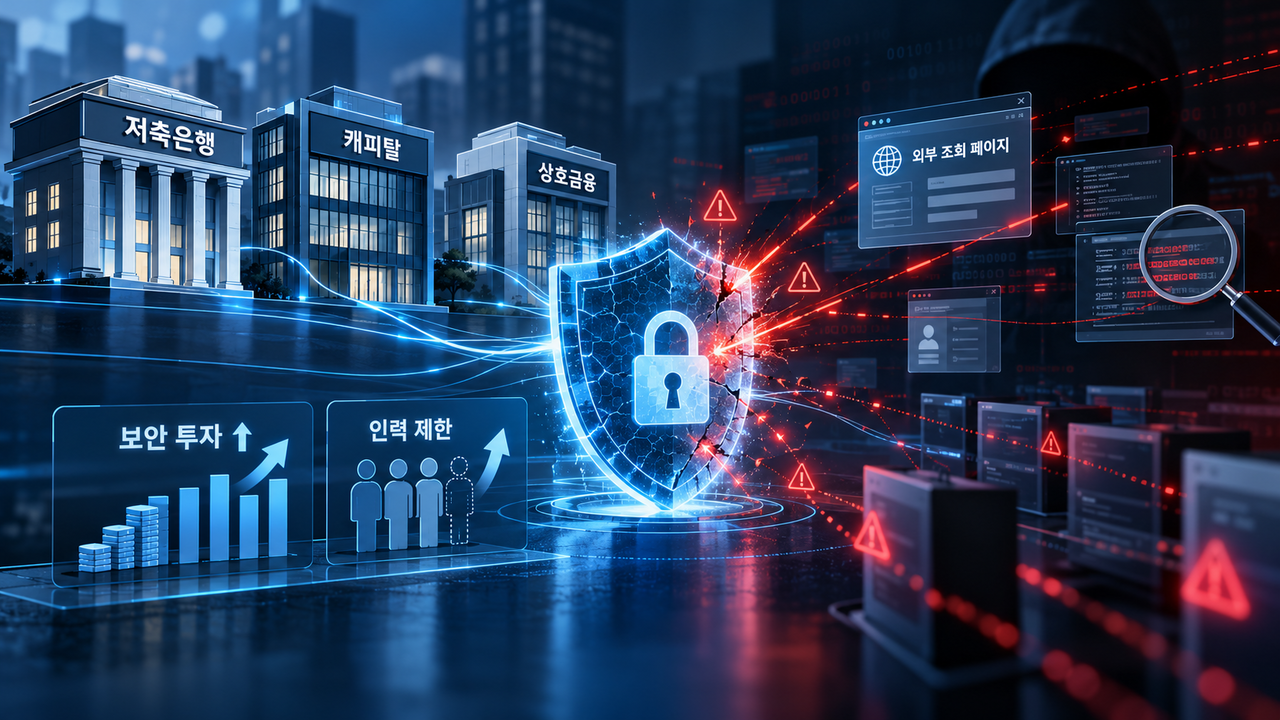
South Korea's second-tier financial institutions are increasing their cybersecurity budgets and staffing in response to a string of hacking incidents, but growing sophistication in attack methods is making it harder to prevent breaches or detect them early. Savings banks in particular lag far behind major commercial banks in both security personnel and investment capacity, and they also carry asset-quality burdens. Industry observers say existing security frameworks are no longer sufficient as attackers increasingly disguise their activity as normal user behavior to evade detection.
Personal data breaches occurred in quick succession recently at Hyundai Capital Services, KDB Capital and OK Savings Bank, according to financial industry sources. The companies discovered the intrusions while reviewing connection logs for suspicious IP addresses flagged by authorities or while commissioning additional investigations by outside security firms. In some cases, the scale of the data leak turned out to be larger than initially assessed.
Hyundai Capital Services, which suffered a breach of 146 personal records through a hacked page used to look up housing loan solicitors, raised its cybersecurity budget this year by about 34 percent from end-2024. The share of cybersecurity spending within its total IT budget rose by 2.42 percentage points over the same period, and the number of dedicated security staff increased by about 47 percent. The company said it has been expanding its cybersecurity budget at a faster pace than its overall IT budget.
Saemaul Geumgo Central, which experienced a breach of member personal data, set aside 16.8 billion won ($12.5 million) for cybersecurity this year — about 2 billion won more than last year. Its dedicated security headcount, however, grew by just one person, from 46 last year to 47 this year.
KDB Capital, which saw 848 customer records leaked, allocated 6.9 billion won of its total IT budget of 45.5 billion won to cybersecurity this year, representing about 15.2 percent of the total. Of that, 2.2 billion won had been spent through the end of June, accounting for about 22.2 percent of the 9.9 billion won in total IT expenditure over the same period. The company has three dedicated security staff.
The gap in security staffing between savings banks and major commercial banks is stark. Data presented by Democratic Party of Korea lawmaker Park Min-gyu at the National Assembly's Financial Services Committee national audit on Thursday showed that the four major commercial banks averaged about 92 dedicated cybersecurity staff, while savings banks averaged just six — a difference of more than 15 times.
According to cybersecurity disclosures by the Korea Internet & Security Agency, Welcome Savings Bank invested 3.75 billion won in cybersecurity last year, with a combined 7.8 dedicated staff — six in-house and 1.8 outsourced. Shinhan Savings Bank invested 1.15 billion won and had 6.1 dedicated staff. The share of cybersecurity investment relative to total IT spending was 15.8 percent at Welcome Savings Bank and 9.8 percent at Shinhan Savings Bank, both above the 8.5 percent average for the four major commercial banks. Even so, the higher spending ratios mask the fact that absolute budgets and staffing levels vary significantly with company size.
A number of savings banks have actually cut their security budgets. Six of the top 10 savings banks by assets reduced their cybersecurity budgets in 2025 from the previous year. OK Savings Bank trimmed its budget by about 30 percent, from 8.1 billion won to 5.7 billion won, and Welcome, DB, Shinhan, Hana and Pepper savings banks also scaled back spending.
Profitability has improved, but asset-quality pressures remain. According to the Financial Supervisory Service, the savings bank sector posted a net profit for the period of 765.8 billion won in the first half of this year, up 508.8 billion won from the same period a year earlier. At the same time, the delinquency rate stood at 6.26 percent at the end of June, up 0.22 percentage points from end-2024. The corporate loan delinquency rate also rose, from 8.00 percent to 8.38 percent over the same period. The sector is effectively being asked to shore up security infrastructure and specialist staff at the same time as it channels funds into managing bad loans.
"Given the difficult operating environment across the industry, it is not easy to simply keep raising security budgets," an official at a credit finance company said. "But as the importance of security grows, we are expanding cybersecurity spending faster than our general IT budget."
The IT operating structure of savings banks also warrants attention. Of the 79 savings banks currently in operation, 67 use the Savings Bank Central Union's integrated financial information system, while the remaining 12 handle core IT operations through their own systems. The shared network can reduce the IT burden on individual savings banks, but industry observers note that security management of online touchpoints — such as websites and external inquiry services — is equally important, and that vulnerabilities in both the shared system and individual services need to be examined together.
Recent breaches have in fact targeted externally exposed inquiry services. Hyundai Capital Services was attacked through its housing loan solicitor lookup page on Sept. 27, leaking the personal information of 146 solicitors, but did not discover the breach until Friday — five days later. The company identified the intrusion while reviewing connection logs for suspicious IP addresses shared by the Financial Security Institute.
KDB Capital also confirmed it had been hacked while analyzing IP addresses flagged by the Financial Security Institute. Investigators found that a test page created during the development of a next-generation system — one that allowed data lookups without a separate authentication step — had remained accessible after the system went live and was exploited in the attack. The incident resulted in the leak of 848 customer records. "We have deleted the page in question and do not expect any further damage," a KDB Capital official said.
At OK Savings Bank, the initial internal assessment and subsequent outside investigations produced different results. The first internal review identified a potential leak of personal data belonging to 183 customers, but follow-up investigations by two external security firms confirmed that 250 customers' information had been compromised. "There were technical shortcomings in the initial internal review that caused us to miss some of the affected records," an OK Savings Bank official said. "The additional checks by outside security firms revealed more victims."
Industry insiders have taken note of a shift in attack methods: unlike past incidents that sought to paralyze systems quickly or flood them with connection attempts, recent attacks approach targets slowly, mimicking the behavior of ordinary users. Because existing security systems are designed to flag anomalies based on abnormal traffic volumes or known attack signatures, they struggle to catch these newer techniques.
"Recently, attackers approach in ways that are hard to distinguish from normal access, and they keep their connection volumes below typical usage levels to avoid triggering alerts," a credit finance industry official said. "The anomaly thresholds built into existing security systems are simply not enough to catch these kinds of attacks."
"Security technology tends to lag behind hacking techniques, so it is never easy to respond every time a new attack method emerges," the official added. "Since attacks are now imitating the behavior of legitimate users, defenders also need to use AI to detect anomalies more precisely."
snsd@heraldcorp.com